Score |
53


Galton
 Student @ University of Lagos


The Internet Is Getting Harder to Defend
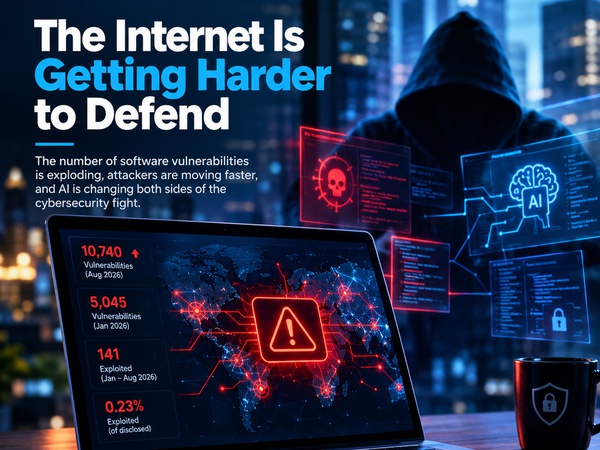
<p>The Internet Is Getting Harder to Defend</p><p><br/></p><p>The number of software vulnerabilities is exploding, attackers are moving faster, and AI is changing both sides of the cybersecurity fight.</p><p><br/></p><p>There was a time when cybersecurity sounded like a problem for large companies with expensive servers.</p><p><br/></p><p>For most people, it meant choosing a strong password, avoiding suspicious emails and installing antivirus software.</p><p><br/></p><p>That world is disappearing.</p><p><br/></p><p>Today, almost everything is connected to something else.</p><p><br/></p><p>Your phone is connected to your email.</p><p><br/></p><p>Your email is connected to your cloud storage.</p><p><br/></p><p>Your bank account is connected to your phone.</p><p><br/></p><p>Businesses connect employees, customers, suppliers, payment systems and thousands of software services.</p><p><br/></p><p>Every connection creates another place where something can go wrong.</p><p><br/></p><p>And the number of things that can go wrong is growing.</p><p><br/></p><p>There are more vulnerabilities than ever</p><p><br/></p><p>Google Threat Intelligence Group recently reported that the number of software vulnerabilities disclosed each month more than doubled during 2026.</p><p><br/></p><p>There were 5,045 vulnerabilities disclosed in January.</p><p><br/></p><p>By August, the number had reached 10,740.</p><p><br/></p><p>That does not mean 10,740 new vulnerabilities were actively being used by criminals. Google makes an important distinction between vulnerabilities that are discovered and vulnerabilities that are actually exploited.</p><p><br/></p><p>Only about 0.23% of vulnerabilities disclosed during 2026 had been observed being exploited in the wild.</p><p><br/></p><p>But even that small percentage represents a serious problem.</p><p><br/></p><p>Google recorded 141 vulnerabilities that were disclosed and exploited between January and August 2026.</p><p><br/></p><p>That was already more than the 127 exploited during the entire year of 2025.</p><p><br/></p><p>The problem is therefore not simply that there are more bugs.</p><p><br/></p><p>It is that attackers have more opportunities to find the few bugs that matter.</p><p><br/></p><p>Finding the hole is only half the race</p><p><br/></p><p>A software vulnerability is essentially a weakness that can be abused.</p><p><br/></p><p>But discovering a weakness does not automatically mean an attacker can exploit it successfully.</p><p><br/></p><p>Someone still has to understand the flaw, develop a working method of exploiting it and find vulnerable systems.</p><p><br/></p><p>Artificial intelligence is beginning to change parts of that process.</p><p><br/></p><p>Google found that AI is measurably changing both the speed and the types of vulnerabilities being discovered.</p><p><br/></p><p>It also found that vulnerabilities identified with the help of AI were more likely to lead to remote code execution than vulnerabilities discovered through other methods.</p><p><br/></p><p>Remote code execution is particularly serious because it can allow an attacker to make a vulnerable system execute commands of their choosing.</p><p><br/></p><p>In simple terms, a small software mistake can become a doorway into an entire machine.</p><p><br/></p><p>The defenders are racing too</p><p><br/></p><p>There is an important side to this story that is sometimes lost in cybersecurity reporting.</p><p><br/></p><p>AI isn't only helping attackers.</p><p><br/></p><p>It is also helping defenders.</p><p><br/></p><p>Security researchers can use AI to inspect code, search for weaknesses, analyse enormous amounts of security data and identify suspicious behaviour.</p><p><br/></p><p>Google's own research describes AI powered vulnerability discovery as part of the changing defensive landscape.</p><p><br/></p><p>That creates an unusual technological race.</p><p><br/></p><p>Attackers are trying to discover and exploit weaknesses faster.</p><p><br/></p><p>Defenders are trying to discover and fix them faster.</p><p><br/></p><p>The winner isn't necessarily the side with the most advanced AI.</p><p><br/></p><p>It may be the side that can move from discovery to action more quickly.</p><p><br/></p><p>The patching problem</p><p><br/></p><p>This is where ordinary software maintenance becomes extremely important.</p><p><br/></p><p>Imagine that a company uses 500 different software products and services.</p><p><br/></p><p>A vulnerability is discovered in one of them.</p><p><br/></p><p>The company now needs to know:</p><p><br/></p><p>Is the affected software installed?</p><p><br/></p><p>Which systems are running it?</p><p><br/></p><p>Are those systems exposed to the internet?</p><p><br/></p><p>Is the vulnerable feature enabled?</p><p><br/></p><p>Has an attacker already tried to exploit it?</p><p><br/></p><p>Is a patch available?</p><p><br/></p><p>Can the patch be installed without breaking something else?</p><p><br/></p><p>This is why cybersecurity is not simply about buying security software.</p><p><br/></p><p>It is also about knowing what you have.</p><p><br/></p><p>You cannot protect systems you don't know exist.</p><p><br/></p><p>Old vulnerabilities can still be dangerous</p><p><br/></p><p>One of the most interesting findings from Google's research is that the growth in exploitation during 2026 has been driven largely by vulnerabilities that were already known.</p><p><br/></p><p>These are sometimes called "n day" vulnerabilities.</p><p><br/></p><p>They are different from zero days because a fix or public information may already exist.</p><p><br/></p><p>That creates a strange situation.</p><p><br/></p><p>A company may technically have a solution available and still remain vulnerable because the patch has not been installed.</p><p><br/></p><p>The attacker doesn't necessarily need a secret vulnerability.</p><p><br/></p><p>They may only need to find somebody who hasn't updated their software.</p><p><br/></p><p>This is one reason cybersecurity can feel unfair.</p><p><br/></p><p>The defender may need to protect thousands of systems perfectly.</p><p><br/></p><p>The attacker may only need to find one neglected system.</p><p><br/></p><p>The weakest link may now be a forgotten device</p><p><br/></p><p>Modern businesses have enormous digital attack surfaces.</p><p><br/></p><p>There are computers, phones, routers, cameras, cloud accounts, collaboration platforms, databases, remote access systems and third party applications.</p><p><br/></p><p>Some devices may be forgotten.</p><p><br/></p><p>Some accounts may belong to former employees.</p><p><br/></p><p>Some servers may still be running old software.</p><p><br/></p><p>Some systems may be exposed to the internet simply because nobody realised they were.</p><p><br/></p><p>Google found that vulnerabilities affecting edge and security appliances represented 14% of vulnerabilities exploited between January and August 2026.</p><p><br/></p><p>These systems are particularly interesting to attackers because they can sit directly between an organisation and the internet.</p><p><br/></p><p>Compromise the right device and an attacker may gain a path into a much larger environment.</p><p><br/></p><p>AI is creating another attack surface</p><p><br/></p><p>There is another problem.</p><p><br/></p><p>While AI is helping security researchers find vulnerabilities, AI systems themselves are becoming software that needs to be secured.</p><p><br/></p><p>Google tracked more than 2,000 vulnerabilities in AI related software between January 2025 and August 2026.</p><p><br/></p><p>Many were associated with AI application infrastructure, including agent orchestration frameworks, model serving systems and enterprise AI gateways.</p><p><br/></p><p>This is an important reminder.</p><p><br/></p><p>Every new technology eventually becomes part of the security problem.</p><p><br/></p><p>We saw it with websites.</p><p><br/></p><p>We saw it with mobile applications.</p><p><br/></p><p>We saw it with cloud computing.</p><p><br/></p><p>Now AI is joining the list.</p><p><br/></p><p>The more businesses connect AI to important systems, the more attractive those systems become to attackers.</p><p><br/></p><p>So what should ordinary people do?</p><p><br/></p><p>The scale of modern cybersecurity can make the problem seem impossible.</p><p><br/></p><p>It isn't.</p><p><br/></p><p>You don't need to become a cybersecurity researcher to make yourself harder to attack.</p><p><br/></p><p>Start with the basics.</p><p><br/></p><p>Keep your operating system and important applications updated.</p><p><br/></p><p>Use unique passwords for important accounts.</p><p><br/></p><p>Use a password manager if you can.</p><p><br/></p><p>Turn on multi factor authentication.</p><p><br/></p><p>Be careful with links received through email, SMS and social media.</p><p><br/></p><p>Review which applications have access to your accounts.</p><p><br/></p><p>Remove applications and accounts you no longer use.</p><p><br/></p><p>Back up important files.</p><p><br/></p><p>And when a service tells you that something needs to be updated, don't automatically treat the notification as an annoyance.</p><p><br/></p><p>Sometimes that update is the thing standing between your data and an attacker.</p><p><br/></p><p>Businesses have an even bigger responsibility</p><p><br/></p><p>For organisations, the lesson is more complicated.</p><p><br/></p><p>Cybersecurity cannot be treated as a department that only becomes important after an incident.</p><p><br/></p><p>Companies need to know what software they are running, what is exposed to the internet, which systems contain sensitive information and which vulnerabilities actually represent meaningful risk.</p><p><br/></p><p>The growing number of vulnerabilities also makes it impossible to treat every security alert as equally urgent.</p><p><br/></p><p>Google's research makes this clear.</p><p><br/></p><p>Thousands of vulnerabilities may be disclosed, but only a tiny fraction are actually observed being exploited.</p><p><br/></p><p>The challenge is therefore not simply finding everything.</p><p><br/></p><p>It is identifying what matters most and acting quickly enough.</p><p><br/></p><p>The internet isn't becoming impossible to defend</p><p><br/></p><p>It is becoming more complicated to defend.</p><p><br/></p><p>There are more devices.</p><p><br/></p><p>More software.</p><p><br/></p><p>More connections.</p><p><br/></p><p>More cloud services.</p><p><br/></p><p>More vulnerabilities.</p><p><br/></p><p>And increasingly, more automation on both sides of the fight.</p><p><br/></p><p>That doesn't mean the internet is doomed.</p><p><br/></p><p>It means cybersecurity has entered a different phase.</p><p><br/></p><p>The old question was:</p><p><br/></p><p>"Is this system secure?"</p><p><br/></p><p>The better question now may be:</p><p><br/></p><p>"How quickly can we discover that it isn't secure, understand the risk and fix it before someone exploits it?"</p><p><br/></p><p>Because in the modern internet, perfection may be impossible.</p><p><br/></p><p>Speed, visibility and resilience may matter just as much.</p><p><br/></p><p>And the organisations that understand that could be the ones that stay standing when the next vulnerability appears.</p>


 58


Other insights from Galton



Contributor Points
Points-to-Coupons

Referral Earning
Insights for you.

My Unpopular opinions of Social Media.
I Really Hate Social MediaWait, hear me out.I'm not saying this from a place of pride o...
230 views
33 upvotes
40 comments

Meet Amina the AI
Well yes, the image attached to this post was created with DALLE. After some interestin...
1472 views
19 upvotes
12 comments

If You Can’t Beat Them, Join Them
I didn’t experience the “before.” Before landlines, before phones, before mobile money—...
319 views
28 upvotes
25 comments

Grandpa lied (A little)
"Grandpa said, farming pays and not even your AI can take that away" that was my cousin...
326 views
25 upvotes
26 comments

Social Media vs Reality – Let’s Be Fo...
Let’s talk. Be honest, have you ever looked at someone’s Instagram story and immediatel...
437 views
15 upvotes
15 comments

Are we becoming who we are, or who we...
We are shaped long before we realize itby things we do not question,by voices we do not...
303 views
19 upvotes
20 comments

Three (3) reasons why AI is losing to...
This article explains how Google's new policy affects AI-written content and flagging g...
822 views
18 upvotes
18 comments

Over sharing with a bot : it's not th...
Lately I’ve realized my most stable relationship might actually be with ChatGPT. 😭 I co...
463 views
16 upvotes
16 comments

The Impact Of Social Media vs Books: ...
A social media personality emerged on the internet months ago and a basic small toy tha...
375 views
19 upvotes
15 comments
Tech is the New White Collar Job
Tech is the New White Collar Job
Tech is the new currency; with tech, you can say cr...
1065 views
17 upvotes
11 comments