Score |
76


Galton
 Student @ University of Lagos


AI Is Finding Security Flaws Faster Than the Internet Can Fix Them
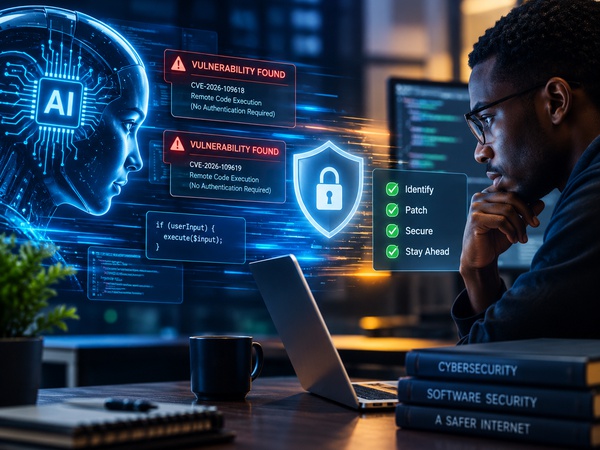
<p><br/></p><p><br/></p><p>Artificial intelligence is changing how software vulnerabilities are discovered. The bigger challenge is whether developers can fix them before attackers take advantage.</p><p><br/></p><p>The internet has a problem that most people never see.</p><p><br/></p><p>Behind the websites we visit, the banking apps we use, and the online services we depend on every day are millions of lines of software. Some are newly written. Others have been running for years, maintained by teams responsible for keeping them secure.</p><p><br/></p><p>Hidden inside that code are weaknesses. Some are harmless mistakes. Others can allow an attacker to steal information, disrupt a service, or take control of a computer remotely.</p><p><br/></p><p>For years, finding these weaknesses required considerable technical expertise, time, and patience.</p><p><br/></p><p>Artificial intelligence is beginning to change that equation.</p><p><br/></p><p>On October 23, 2026, Reuters reported that AI-assisted vulnerability discovery was contributing to a growing stream of newly identified software flaws. Research from cybersecurity intelligence firm VulnCheck indicated that the number of discovered digital vulnerabilities had doubled year over year, with AI identified as one contributing factor.</p><p><br/></p><p>The implications extend beyond cybersecurity teams. When vulnerabilities are discovered faster than organisations can fix them, the consequences can reach businesses, public institutions, and ordinary internet users.</p><p><br/></p><p>The emerging problem is not simply that AI can find software weaknesses. It is that discovering weaknesses and fixing them are two very different jobs.</p><p><br/></p><p>"Source: Reuters, October 23, 2026" (<a class="tc-blue" href="https://www.reuters.com/legal/litigation/ai-discovered-bugs-may-soon-trigger-fresh-disruptions-cyber-experts-say-2026-10-23/)" rel="noopener noreferrer" target="_blank">www.reuters.com/legal/litigation/ai-d... </a></p><p><br/></p><p>The Problem Hidden Inside the Software We Use</p><p><br/></p><p>To understand why this matters, consider how a typical website works.</p><p><br/></p><p>When you visit a website, your browser communicates with a server. That server processes requests, retrieves information, and sends the appropriate response.</p><p><br/></p><p>Behind the scenes, different software components work together to make this possible.</p><p><br/></p><p>A website might depend on a content management system, a programming language, a database, external libraries, and several other services. Even if the website's owner writes excellent code, a vulnerability in one of these underlying components can put the entire service at risk.</p><p><br/></p><p>This is one reason software security is so difficult.</p><p><br/></p><p>A weakness does not necessarily belong to the organisation whose website is affected. It might exist in a programming language, a third-party library, or another component that thousands of organisations use.</p><p><br/></p><p>And if a vulnerable component is widely deployed, one security flaw can potentially expose many different systems.</p><p><br/></p><p>That is precisely why the speed at which vulnerabilities are discovered matters.</p><p><br/></p><p>AI Is Changing the Economics of Finding Vulnerabilities</p><p><br/></p><p>Traditionally, vulnerability discovery has relied heavily on security researchers examining code, testing software behaviour, and investigating unusual results.</p><p><br/></p><p>Artificial intelligence can assist with several parts of this process.</p><p><br/></p><p>Depending on the tools and the software involved, AI systems can help researchers:</p><p><br/></p><p>- Examine large codebases for suspicious patterns.</p><p>- Identify potentially unsafe ways of handling data.</p><p>- Suggest test cases that developers might not have considered.</p><p>- Investigate how different software components interact.</p><p>- Analyse errors and help researchers understand their causes.</p><p>- Assist in developing proof-of-concept tests to determine whether a suspected weakness is real.</p><p><br/></p><p>These capabilities do not mean that AI automatically finds every vulnerability or that every result it produces is correct. Researchers must still validate findings, understand the affected systems, and determine whether a weakness can actually be exploited.</p><p><br/></p><p>Nevertheless, AI can reduce the amount of manual work required to investigate some classes of software defects.</p><p><br/></p><p>The consequences are significant.</p><p><br/></p><p>A vulnerability that might previously have taken considerable time to identify could become easier to discover. Security researchers could examine more software, while organisations could use similar techniques to test their own systems.</p><p><br/></p><p>But the same general capabilities could also benefit malicious actors.</p><p><br/></p><p>The technology does not inherently distinguish between someone searching for a vulnerability to fix it and someone searching for a vulnerability to exploit it.</p><p><br/></p><p>That is where the security challenge begins.</p><p><br/></p><p>A Critical PHP Security Warning Shows What Is at Stake</p><p><br/></p><p>Consider what happened this week.</p><p><br/></p><p>On October 21, the PHP development team released security updates addressing two critical vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619.</p><p><br/></p><p>The vulnerabilities could allow remote code execution without authentication on affected systems.</p><p><br/></p><p>In plain English, remote code execution means a vulnerability could enable an attacker to make a vulnerable system execute malicious instructions. The absence of an authentication requirement makes such a weakness particularly serious because the attacker may not need a legitimate account to initiate an attack.</p><p><br/></p><p>The PHP team released fixes in versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35.</p><p><br/></p><p>The United States Cybersecurity and Infrastructure Security Agency (CISA) urged organisations to apply the updates immediately, prioritising systems exposed to the internet.</p><p><br/></p><p>On October 23, European cybersecurity authorities also updated their guidance concerning the PHP vulnerabilities.</p><p><br/></p><p>These developments illustrate how a software weakness can become an urgent operational problem. Organisations must identify affected systems, determine which software versions they use, apply the appropriate updates, and verify that their systems are protected.</p><p><br/></p><p>However, an important distinction is necessary: the PHP security advisories establish the existence and seriousness of the vulnerabilities, but they do not establish that AI discovered those particular flaws. The PHP incident is an example of the wider security pressures facing internet infrastructure, not proof that AI caused this specific incident.</p><p><br/></p><p>Sources:</p><p><br/></p><p>- "Official PHP security advisory" (<a class="tc-blue" href="https://www.php.net/archive/2026.php)" rel="noopener noreferrer" target="_blank">www.php.net/archive/2026.php) </a></p><p>- "CISA security alert" (<a class="tc-blue" href="https://content.govdelivery.com/accounts/USDHSCISA/bulletins/42ff5ac)" rel="noopener noreferrer" target="_blank">content.govdelivery.com/accounts/USDH... </a></p><p>- "European Union Agency for Cybersecurity (ENISA)" (<a class="tc-blue" href="https://www.enisa.europa.eu/news/joint-statement-on-critical-php-vulnerabilities)" rel="noopener noreferrer" target="_blank">www.enisa.europa.eu/news/joint-statem... </a></p><p><br/></p><p>The Race Between Discovery and Repair</p><p><br/></p><p>Finding a vulnerability does not automatically make a system vulnerable to an immediate attack. Nor does every discovered flaw become a practical weapon for cybercriminals.</p><p><br/></p><p>But the period between discovery and repair can be dangerous.</p><p><br/></p><p>Once a vulnerability becomes known, developers need to investigate it and produce a fix. Organisations must then determine whether they are affected and deploy the update.</p><p><br/></p><p>That process can take time.</p><p><br/></p><p>A company operating a small website might be able to update its software quickly. A bank, government agency, or large business could have hundreds of interconnected systems, compatibility requirements, and approval procedures to navigate.</p><p><br/></p><p>Some organisations may not even know that a vulnerable component exists within their infrastructure.</p><p><br/></p><p>Meanwhile, attackers can investigate the same vulnerability, search for exposed systems, and attempt to develop ways to exploit it.</p><p><br/></p><p>AI could intensify this race by helping researchers and attackers investigate software weaknesses more efficiently.</p><p><br/></p><p>The risk is not simply that vulnerabilities will be discovered. It is that defenders may have less time to respond before attackers can take advantage of them.</p><p><br/></p><p>This is not inevitable in every case. Some vulnerabilities are difficult to exploit, and security researchers can use AI to improve detection, testing, and remediation too.</p><p><br/></p><p>Nevertheless, organisations cannot assume that their existing response processes will remain adequate as the pace of vulnerability discovery changes.</p><p><br/></p><p>What This Means for Nigeria</p><p><br/></p><p>Nigeria's digital economy depends on software in ways that are easy to overlook.</p><p><br/></p><p>Banks and fintech companies rely on interconnected systems to process transactions. Online retailers depend on websites and payment services. Universities operate digital portals. Businesses use cloud applications to manage customers, records, and payments.</p><p><br/></p><p>Publishers also depend on this infrastructure.</p><p><br/></p><p>A website might look simple from the outside, but its security depends on its hosting environment, software, extensions, configuration, and maintenance practices.</p><p><br/></p><p>For a Nigerian business, the consequences of a security failure could include service disruption, loss of access to important records, exposure of customer information, financial damage, and reputational harm.</p><p><br/></p><p>Smaller organisations can face particular difficulties because they may lack dedicated cybersecurity personnel.</p><p><br/></p><p>The problem is not that Nigerian organisations are uniquely exposed to AI-driven vulnerabilities. It is that the same global software weaknesses can affect organisations regardless of their location, while their ability to respond depends on their resources and security practices.</p><p><br/></p><p>This makes routine maintenance more important, not less.</p><p><br/></p><p>A business does not need to develop sophisticated AI systems to improve its security. It needs to understand what software it depends on, keep that software supported, apply important security updates promptly, and know who is responsible when something goes wrong.</p><p><br/></p><p>For website administrators, that includes asking a hosting provider questions that might otherwise go unanswered:</p><p><br/></p><p>- Which PHP version is my website running?</p><p>- Is that version still receiving security updates?</p><p>- Who is responsible for applying critical server updates?</p><p>- How quickly will the hosting provider respond to a serious vulnerability?</p><p>- Are backups available if the website needs to be restored?</p><p><br/></p><p>These are practical questions, not merely technical formalities.</p><p><br/></p><p>What Website Owners and Businesses Should Do</p><p><br/></p><p>The growing role of AI in vulnerability discovery is a reason to strengthen basic security practices.</p><p><br/></p><p>It is not a reason to panic or assume that every website is about to be compromised.</p><p><br/></p><p>Here are five measures organisations should prioritise.</p><p><br/></p><p>1. Know What Your Systems Are Running</p><p><br/></p><p>You cannot protect software you do not know you have.</p><p><br/></p><p>Maintain an inventory of important systems, programming languages, applications, plugins, and third-party components.</p><p><br/></p><p>For websites, check whether the hosting provider can identify the software versions running on the server.</p><p><br/></p><p>2. Apply Security Updates Promptly</p><p><br/></p><p>Updates are not always about new features or visual improvements. Some exist specifically to correct weaknesses that could compromise a system.</p><p><br/></p><p>Organisations should monitor official security announcements and prioritise patches according to the severity of the vulnerability and the exposure of the affected system.</p><p><br/></p><p>For the PHP vulnerabilities disclosed on October 21, the PHP development team identified the patched versions in its official advisory.</p><p><br/></p><p>Website owners should confirm their actual server configuration with their hosting provider rather than assuming that updating a website's content management system automatically updates the underlying server software.</p><p><br/></p><p>3. Stop Depending on Unsupported Software</p><p><br/></p><p>Software that no longer receives security updates can become a persistent liability.</p><p><br/></p><p>Organisations should plan upgrades away from unsupported versions and products. If an urgent vulnerability affects a system that cannot be patched, they should follow authoritative security guidance on isolating or temporarily taking the affected service offline.</p><p><br/></p><p>A security warning should trigger an assessment, not an assumption that a system is safe simply because it still works.</p><p><br/></p><p>4. Maintain Reliable Backups</p><p><br/></p><p>Backups cannot prevent every cyberattack, but they can help an organisation recover from certain incidents.</p><p><br/></p><p>Keep backups of essential data and configurations, protect them against unauthorised modification, and test whether they can actually be restored.</p><p><br/></p><p>A backup that has never been tested is not a dependable recovery strategy.</p><p><br/></p><p>5. Give Someone Clear Responsibility for Security</p><p><br/></p><p>Security failures are not always caused by a lack of available technology.</p><p><br/></p><p>Sometimes, no one knows who is responsible for monitoring vulnerabilities, approving updates, or checking whether a fix was successfully applied.</p><p><br/></p><p>Every organisation should establish clear responsibility for these tasks, whether they are handled internally or by an external service provider.</p><p><br/></p><p>For businesses without dedicated security teams, a competent hosting provider or qualified IT professional can help establish a realistic maintenance process.</p><p><br/></p><p>AI Can Also Help Defenders</p><p><br/></p><p>It would be misleading to present AI as a technology that only benefits attackers.</p><p><br/></p><p>Security teams can use AI-assisted tools to examine code, identify suspicious behaviour, prioritise vulnerabilities, support incident investigations, and help developers understand potential fixes.</p><p><br/></p><p>AI could make security testing more accessible to organisations that previously lacked the resources to conduct extensive manual reviews.</p><p><br/></p><p>It could also help software developers identify defects earlier, before vulnerable code reaches production systems.</p><p><br/></p><p>But these benefits depend on how the technology is deployed.</p><p><br/></p><p>An AI-generated finding must be verified. A proposed fix must be tested. Automated security tools need appropriate permissions and oversight. Organisations must also protect sensitive code and data when using external AI services.</p><p><br/></p><p>Most importantly, identifying more vulnerabilities does not automatically mean fixing more of them.</p><p><br/></p><p>If AI helps an organisation discover a thousand potential weaknesses but the organisation lacks the people, processes, or resources to investigate and repair them, the technology may expose a capacity problem rather than solve it.</p><p><br/></p><p>The objective should not be to discover vulnerabilities as quickly as possible in isolation.</p><p><br/></p><p>It should be to reduce the time between identifying a genuine security problem and making the affected system safe.</p><p><br/></p><p>The Real Test Is Whether We Can Keep Up</p><p><br/></p><p>The internet was not built in a single day, and its security weaknesses will not disappear overnight.</p><p><br/></p><p>It has evolved through decades of software development, accumulated technical decisions, and systems that must continue operating even as new threats emerge.</p><p><br/></p><p>AI is adding a new dimension to that challenge.</p><p><br/></p><p>The technology could help security researchers uncover defects that would otherwise remain hidden. It could also help malicious actors investigate weaknesses more efficiently.</p><p><br/></p><p>The final outcome will depend partly on how effectively software developers, hosting providers, businesses, governments, and security professionals respond.</p><p><br/></p><p>One conclusion is already clear: organisations cannot rely on the assumption that a vulnerability will remain obscure simply because nobody has reported it yet.</p><p><br/></p><p>Security must become a continuous process of discovery, verification, repair, and monitoring.</p><p><br/></p><p>For website owners and businesses, that means taking software maintenance seriously before a security warning arrives.</p><p><br/></p><p>For developers, it means treating secure coding and timely patching as essential responsibilities rather than optional improvements.</p><p><br/></p><p>And for users, it means recognising that the safety of a digital service depends on far more than the interface they see on their screens.</p><p><br/></p><p>AI may be making it easier to find the cracks in the internet. Whether those cracks become disasters will depend on how quickly we learn to repair them.</p><p><br/></p><p>Sources and Further Reading</p><p><br/></p><p>1. "Reuters: AI-discovered bugs may soon trigger fresh disruptions, cyber experts say" (<a class="tc-blue" href="https://www.reuters.com/legal/litigation/ai-discovered-bugs-may-soon-trigger-fresh-disruptions-cyber-experts-say-2026-10-23/)" rel="noopener noreferrer" target="_blank">www.reuters.com/legal/litigation/ai-d... </a></p><p>2. "PHP: Official 2026 security announcements" (<a class="tc-blue" href="https://www.php.net/archive/2026.php)" rel="noopener noreferrer" target="_blank">www.php.net/archive/2026.php) </a></p><p>3. "CISA: Critical vulnerabilities in PHP require immediate patching" (<a class="tc-blue" href="https://content.govdelivery.com/accounts/USDHSCISA/bulletins/42ff5ac)" rel="noopener noreferrer" target="_blank">content.govdelivery.com/accounts/USDH... </a></p><p>4. "ENISA: Joint statement on critical PHP vulnerabilities" (<a class="tc-blue" href="https://www.enisa.europa.eu/news/joint-statement-on-critical-php-vulnerabilities)" rel="noopener noreferrer" target="_blank">www.enisa.europa.eu/news/joint-statem... </a></p><p><br/></p><p>About This Article</p><p><br/></p><p>This article distinguishes between documented PHP vulnerabilities, reported trends in AI-assisted vulnerability discovery, and potential future risks. The reported year-on-year doubling of discovered digital flaws is attributed to research cited by Reuters; it should not be interpreted as proof that AI alone caused the increase or that successful cyberattacks have doubled.</p>


 75


Other insights from Galton



Contributor Points
Points-to-Coupons

Referral Earning
Insights for you.

My Unpopular opinions of Social Media.
I Really Hate Social MediaWait, hear me out.I'm not saying this from a place of pride o...
251 views
33 upvotes
40 comments
New York City bans AI for children.
AI is a very powerful tool.But should young children have unrestricted access to it?On ...
106 views
29 upvotes
34 comments

Meet Amina the AI
Well yes, the image attached to this post was created with DALLE. After some interestin...
1490 views
20 upvotes
12 comments

If You Can’t Beat Them, Join Them
I didn’t experience the “before.” Before landlines, before phones, before mobile money—...
340 views
28 upvotes
25 comments

Grandpa lied (A little)
"Grandpa said, farming pays and not even your AI can take that away" that was my cousin...
345 views
25 upvotes
26 comments

Social Media vs Reality – Let’s Be Fo...
Let’s talk. Be honest, have you ever looked at someone’s Instagram story and immediatel...
454 views
15 upvotes
15 comments

Are we becoming who we are, or who we...
We are shaped long before we realize itby things we do not question,by voices we do not...
322 views
19 upvotes
20 comments

Three (3) reasons why AI is losing to...
This article explains how Google's new policy affects AI-written content and flagging g...
859 views
18 upvotes
18 comments

Over sharing with a bot : it's not th...
Lately I’ve realized my most stable relationship might actually be with ChatGPT. 😭 I co...
477 views
16 upvotes
16 comments

The Impact Of Social Media vs Books: ...
A social media personality emerged on the internet months ago and a basic small toy tha...
405 views
19 upvotes
15 comments