

The Internet Is Getting Harder to Defend
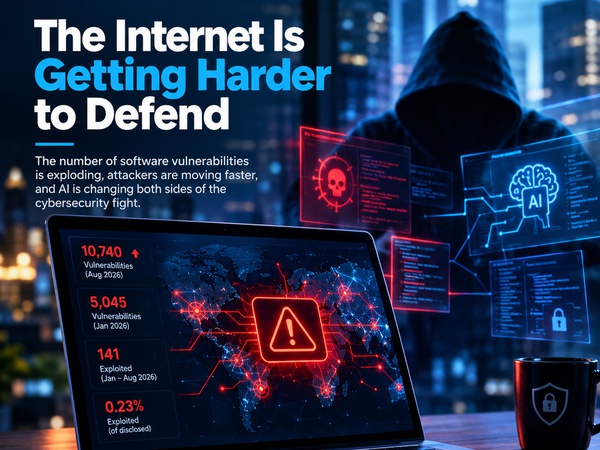
The number of software vulnerabilities is exploding, attackers are moving faster, and AI is changing both sides of the cybersecurity fight.
There was a time when cybersecurity sounded like a problem for large companies with expensive servers.
For most people, it meant choosing a strong password, avoiding suspicious emails and installing antivirus software.
That world is disappearing.
Today, almost everything is connected to something else.
Your phone is connected to your email.
Your email is connected to your cloud storage.
Your bank account is connected to your phone.
Businesses connect employees, customers, suppliers, payment systems and thousands of software services.
Every connection creates another place where something can go wrong.
And the number of things that can go wrong is growing.
There are more vulnerabilities than ever
Google Threat Intelligence Group recently reported that the number of software vulnerabilities disclosed each month more than doubled during 2026.
There were 5,045 vulnerabilities disclosed in January.
By August, the number had reached 10,740.
That does not mean 10,740 new vulnerabilities were actively being used by criminals. Google makes an important distinction between vulnerabilities that are discovered and vulnerabilities that are actually exploited.
Only about 0.23% of vulnerabilities disclosed during 2026 had been observed being exploited in the wild.
But even that small percentage represents a serious problem.
Google recorded 141 vulnerabilities that were disclosed and exploited between January and August 2026.
That was already more than the 127 exploited during the entire year of 2025.
The problem is therefore not simply that there are more bugs.
It is that attackers have more opportunities to find the few bugs that matter.
Finding the hole is only half the race
A software vulnerability is essentially a weakness that can be abused.
But discovering a weakness does not automatically mean an attacker can exploit it successfully.
Someone still has to understand the flaw, develop a working method of exploiting it and find vulnerable systems.
Artificial intelligence is beginning to change parts of that process.
Google found that AI is measurably changing both the speed and the types of vulnerabilities being discovered.
It also found that vulnerabilities identified with the help of AI were more likely to lead to remote code execution than vulnerabilities discovered through other methods.
Remote code execution is particularly serious because it can allow an attacker to make a vulnerable system execute commands of their choosing.
In simple terms, a small software mistake can become a doorway into an entire machine.
The defenders are racing too
There is an important side to this story that is sometimes lost in cybersecurity reporting.
AI isn't only helping attackers.
It is also helping defenders.
Security researchers can use AI to inspect code, search for weaknesses, analyse enormous amounts of security data and identify suspicious behaviour.
Google's own research describes AI powered vulnerability discovery as part of the changing defensive landscape.
That creates an unusual technological race.
Attackers are trying to discover and exploit weaknesses faster.
Defenders are trying to discover and fix them faster.
The winner isn't necessarily the side with the most advanced AI.
It may be the side that can move from discovery to action more quickly.
The patching problem
This is where ordinary software maintenance becomes extremely important.
Imagine that a company uses 500 different software products and services.
A vulnerability is discovered in one of them.
The company now needs to know:
Is the affected software installed?
Which systems are running it?
Are those systems exposed to the internet?
Is the vulnerable feature enabled?
Has an attacker already tried to exploit it?
Is a patch available?
Can the patch be installed without breaking something else?
This is why cybersecurity is not simply about buying security software.
It is also about knowing what you have.
You cannot protect systems you don't know exist.
Old vulnerabilities can still be dangerous
One of the most interesting findings from Google's research is that the growth in exploitation during 2026 has been driven largely by vulnerabilities that were already known.
These are sometimes called "n day" vulnerabilities.
They are different from zero days because a fix or public information may already exist.
That creates a strange situation.
A company may technically have a solution available and still remain vulnerable because the patch has not been installed.
The attacker doesn't necessarily need a secret vulnerability.
They may only need to find somebody who hasn't updated their software.
This is one reason cybersecurity can feel unfair.
The defender may need to protect thousands of systems perfectly.
The attacker may only need to find one neglected system.
The weakest link may now be a forgotten device
Modern businesses have enormous digital attack surfaces.
There are computers, phones, routers, cameras, cloud accounts, collaboration platforms, databases, remote access systems and third party applications.
Some devices may be forgotten.
Some accounts may belong to former employees.
Some servers may still be running old software.
Some systems may be exposed to the internet simply because nobody realised they were.
Google found that vulnerabilities affecting edge and security appliances represented 14% of vulnerabilities exploited between January and August 2026.
These systems are particularly interesting to attackers because they can sit directly between an organisation and the internet.
Compromise the right device and an attacker may gain a path into a much larger environment.
AI is creating another attack surface
There is another problem.
While AI is helping security researchers find vulnerabilities, AI systems themselves are becoming software that needs to be secured.
Google tracked more than 2,000 vulnerabilities in AI related software between January 2025 and August 2026.
Many were associated with AI application infrastructure, including agent orchestration frameworks, model serving systems and enterprise AI gateways.
This is an important reminder.
Every new technology eventually becomes part of the security problem.
We saw it with websites.
We saw it with mobile applications.
We saw it with cloud computing.
Now AI is joining the list.
The more businesses connect AI to important systems, the more attractive those systems become to attackers.
So what should ordinary people do?
The scale of modern cybersecurity can make the problem seem impossible.
It isn't.
You don't need to become a cybersecurity researcher to make yourself harder to attack.
Start with the basics.
Keep your operating system and important applications updated.
Use unique passwords for important accounts.
Use a password manager if you can.
Turn on multi factor authentication.
Be careful with links received through email, SMS and social media.
Review which applications have access to your accounts.
Remove applications and accounts you no longer use.
Back up important files.
And when a service tells you that something needs to be updated, don't automatically treat the notification as an annoyance.
Sometimes that update is the thing standing between your data and an attacker.
Businesses have an even bigger responsibility
For organisations, the lesson is more complicated.
Cybersecurity cannot be treated as a department that only becomes important after an incident.
Companies need to know what software they are running, what is exposed to the internet, which systems contain sensitive information and which vulnerabilities actually represent meaningful risk.
The growing number of vulnerabilities also makes it impossible to treat every security alert as equally urgent.
Google's research makes this clear.
Thousands of vulnerabilities may be disclosed, but only a tiny fraction are actually observed being exploited.
The challenge is therefore not simply finding everything.
It is identifying what matters most and acting quickly enough.
The internet isn't becoming impossible to defend
It is becoming more complicated to defend.
There are more devices.
More software.
More connections.
More cloud services.
More vulnerabilities.
And increasingly, more automation on both sides of the fight.
That doesn't mean the internet is doomed.
It means cybersecurity has entered a different phase.
The old question was:
"Is this system secure?"
The better question now may be:
"How quickly can we discover that it isn't secure, understand the risk and fix it before someone exploits it?"
Because in the modern internet, perfection may be impossible.
Speed, visibility and resilience may matter just as much.
And the organisations that understand that could be the ones that stay standing when the next vulnerability appears.


 239